DevOps · CI/CD
Ship with confidence: a CI/CD pipeline with GitHub Actions
Every change is tested, built and deployed automatically, with no manual steps and no surprises in production.
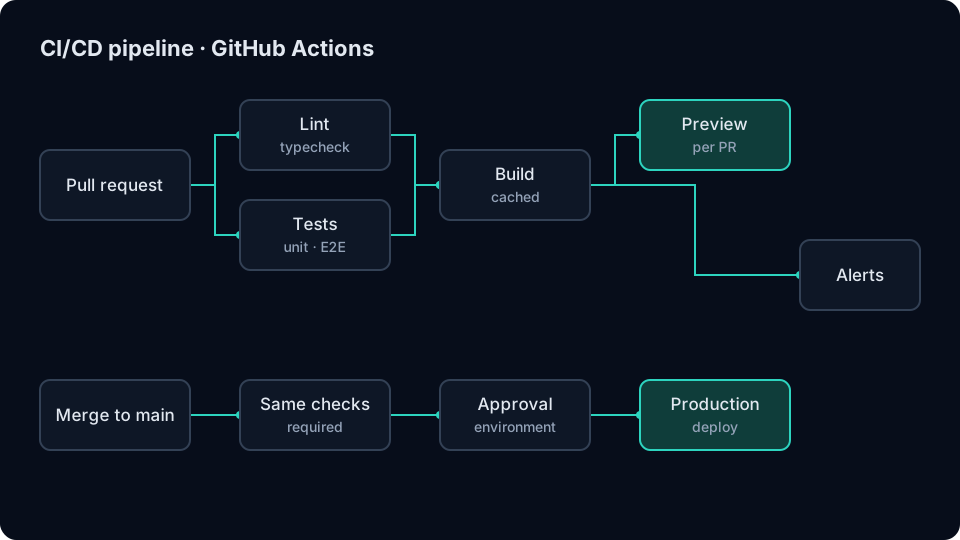
If deploying today depends on one person, a checklist or crossed fingers, every release is a risk. I design and build a GitHub Actions pipeline that runs linting, tests and the build on every pull request, publishes preview environments and deploys to production repeatably, with secrets kept out of the repository.
- GitHub Actions
- Continuous integration
- Continuous deployment
- Automated testing
Gallery
Packages
Three levels of scope. Pricing is quoted for your case.
Basic
Continuous integration for one repository, so no broken change reaches the main branch.
Deliverables
- GitHub Actions workflow running linting, tests and the build on every pull request
- Dependency caching for fast runs
- Required status checks on the main branch
- Short documentation in the README
- Estimated delivery: 3 days
- 1 revision
Standard
Continuous integration and deployment to staging and production, with approvals and properly managed secrets.
Deliverables
- Everything in Basic
- Automatic deployment to staging and production
- Secrets and approvals with GitHub Environments
- Alerts when the pipeline fails
- Estimated delivery: 7 days
- 2 revisions
Premium
A complete delivery platform for your team, with preview environments and reusable workflows.
Deliverables
- Everything in Standard
- A preview environment for every pull request
- Reusable workflows and composite actions across repositories
- A documented rollback strategy
- A handover session with your team
- Estimated delivery: 14 days
- 3 revisions
Related work
Past projects where I did this kind of work. Clients stay anonymous for confidentiality.
Open-source integration platform · United States
Automated quality checks for a catalog of thousands of integrations
Node.js developer · 4+ years
- Problem
- The platform publishes components (sources and actions) that connect to more than 3,000 apps. When a change affected a component, directly or through shared dependencies, it was easy to forget to bump its version, and errors in integrated apps were hard to spot among so many.
- Solution
- I built a GitHub Action that walks the dependency tree of the changed files and checks that every affected component has a new version, and a GitHub workflow that monitors errors across the more than 3,000 integrated apps. I also developed new source and action components for the platform.
- Result
- Missing version bumps are caught in the pull request itself, before publishing, and errors in integrated apps are reported by an automated workflow instead of manual review.
- Node.js
- JavaScript
- TypeScript
- GitHub Actions
- REST APIs
What I need from you
- Repository access with maintainer or admin role
- How the application is built and deployed today
- Credentials for the target environment with only the permissions needed
- A technical contact person for questions
Frequently asked questions
Does my code need to be on GitHub?
Yes, the pipeline runs on GitHub Actions. If your code lives elsewhere, the migration can be part of the proposal.
Will it work with my stack?
GitHub Actions supports most languages and platforms (Node.js, Python, Docker and more). We confirm it during the initial diagnosis.
Who pays for the GitHub Actions minutes?
The workflows run on your account. I design them with caching and conditions to avoid unnecessary runs.
What if I need changes after delivery?
Every package includes revision rounds. For ongoing support we can agree on a separate plan.